In the dynamic digital realm, every click and keystroke resonates across cyberspace. The ongoing battle for data security places businesses as both guardians and targets, with unseen adversaries eyeing their digital assets.
Navigating this challenging landscape demands a dual-sided strategy. Businesses must equip themselves with a sophisticated cybersecurity arsenal, featuring vigilant preventive measures on one side (Left of Boom) and resilient recovery defenses on the other (Right of Boom).
Together, these strategies serve as the linchpin for a comprehensive defense, ensuring businesses can thwart attacks and emerge stronger from any breaches.
This blog post elucidates how to structure your cybersecurity approach into Left and Right of Boom.
What Do “Left of Boom” and “Right of Boom” Mean?
In the realm of cybersecurity, “Left of Boom” and “Right of Boom” are strategic terms. They delineate the proactive and reactive approaches to dealing with cyber threats
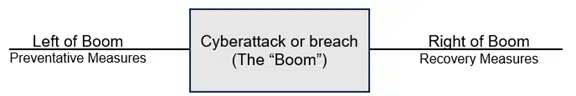
“Left of Boom” refers to preemptive measures and preventative strategies. These are things implemented to safeguard against potential security breaches. It encompasses actions aimed at preventing cyber incidents before they occur.
“Right of Boom” pertains to the post-breach recovery strategies. Companies use these after a security incident has taken place. This phase involves activities like incident response planning and data backup.
Collectively, these terms constitute a holistic cybersecurity strategy, encompassing both prevention and recovery elements. The objective is to bolster an organisation’s resilience against cyber threats.
Left of Boom: Prevention Strategies
User Education and Awareness
A cornerstone of Left of Boom is educating employees on cybersecurity. Regular training sessions empower staff to identify phishing emails, recognize social engineering attempts, and adopt secure online behaviors. An informed workforce becomes a robust line of defense against potential threats.
Employee training lowers the risk of falling for a phishing attack by 75%.
Robust Access Control and Authentication
Enforcing stringent access control measures minimizes the risk of a breach, ensuring that employees have access only to tools essential for their roles.
Access control tactics encompass:
- Least privilege access
- Multifactor authentication (MFA)
- Contextual access
- Single Sign-on (SSO) solutions
Regular Software Updates and Patch Management
Cybercriminals often target outdated software vulnerabilities. Left of Boom strategies involve ensuring regular updates for all software, incorporating the latest security patches. Automated patch management tools can streamline this process, minimising the window of vulnerability.
Network Security and Firewalls
Firewalls serve as the initial defense against external threats. Deploy strong firewalls and intrusion detection/prevention systems to monitor network traffic and detect suspicious activities. They also thwart unauthorized access attempts. Maintaining secure network configurations is crucial to prevent unauthorised access to sensitive data.
Regular Security Audits and Vulnerability Assessments
Perform routine security audits and vulnerability assessments to uncover potential weaknesses in your systems. Proactively addressing these vulnerabilities enables organisations to mitigate risk and decrease the likelihood of exploitation by cybercriminals. Additionally, penetration testing simulates real-world cyber-attacks, providing businesses with an effective evaluation of their security posture.
Right of Boom: Recovery Strategies
Incident Response Plan
Having a well-defined incident response plan in place is crucial. This plan should outline the steps to take in the event of a security breach.
It should include things like:
- Communication protocols
- Containment procedures
- Steps for recovery
- IT contact numbers
Regularly test and update your incident response plan. This ensures it remains effective and relevant.
Data Backup and Disaster Recovery
Consistently backing up data is a crucial element of the Right of Boom. Equally important is having a strong disaster recovery plan in place.
Automated backup systems guarantee the regular backup of critical data, ensuring quick restoration in case of a breach. A well-prepared disaster recovery plan enables businesses to swiftly resume operations after an incident.
Forensic Analysis and Learning
Following a security breach, perform a comprehensive forensic analysis to comprehend the attack’s nature, assess the extent of damage, and identify the exploited vulnerabilities.
Extracting lessons from such incidents empowers organisations to fortify their security posture, increasing resilience against similar future attacks.
Legal and Regulatory Compliance
After a security breach, understanding and adhering to legal and regulatory obligations are crucial. Organisations must comply with data breach notification laws and regulations, emphasising timely and transparent communication with affected parties. This is essential for preserving trust and credibility.
Get Help with a Strong 2-pronged Cybersecurity Strategy
Incorporating Left and Right of Boom strategies enhances your security position, addressing critical aspects of a robust defense.
For assistance in getting started, feel free to reach out and schedule a discussion with us today.